Services /Endpoint Security

Endpoint Security

Anti-malware, anti-ransomware and device control on every laptop, desktop and server.

Overview

What we deliver

Managed endpoint protection that helps block malware, ransomware and other threats — combined with device control, URL filtering and vulnerability assessment under one monitored security service.

  • AI and behaviour-based anti-malware
  • Dedicated anti-ransomware with automatic rollback
  • Vulnerability assessment and patch management
  • Device and USB control
  • URL filtering and exploit prevention
  • Lightweight endpoint security agent
Endpoint protection across office laptops
Problems we solve
  • Signature-only antivirus missing modern malware
  • Ransomware reaching business-critical files
  • Unpatched software left exposed for weeks
  • Multiple agents slowing devices down

Outcomes

What you can expect

Ransomware stopped and reversed

Fewer infected devices to rebuild

Clear threat visibility and response

At a glance

Endpoint Security explained

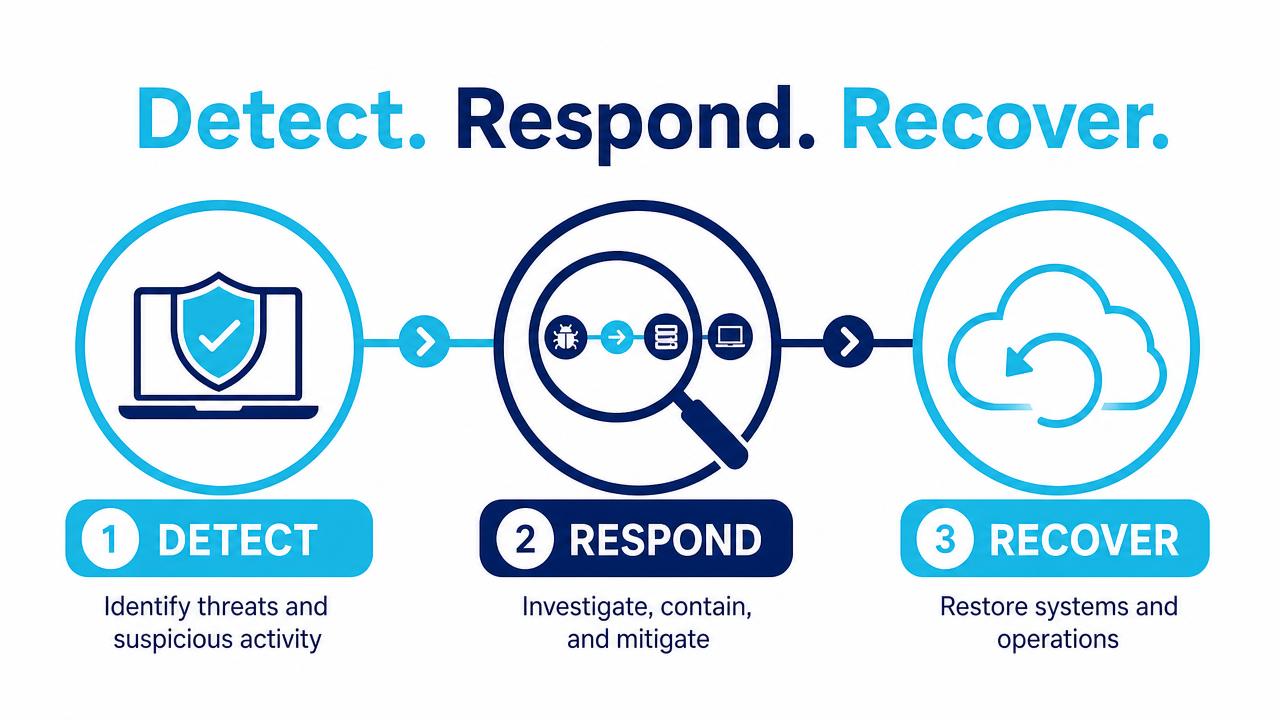
Detect, respond and recover stages of NG TELECOM managed security

How NG TELECOM detects, responds to and recovers from an attack.

In depth

How the service works

Managed endpoint protection without unnecessary complexity

NG TELECOM uses Trend Micro-led endpoint security to monitor and protect business devices against malware, ransomware and suspicious behaviour. Policies, alerts and response actions are managed as part of the service, while backup and recovery remain a separate, coordinated protection layer.

Behavioural detection, not signature roulette

Modern endpoint security analyses behaviour as well as known indicators, helping identify suspicious activity that traditional signature-only tools can miss. Our team monitors the resulting alerts and coordinates containment, remediation and recovery when required.

Vulnerabilities closed on a schedule

Every endpoint is scanned for missing operating system and third-party application patches across Windows, macOS and Linux. Patches are approved, staged and deployed on an agreed maintenance window, with an automatic backup taken before patching so a bad update never becomes an outage.

Independently validated protection

The engines we deploy are assessed continuously by independent labs including AV-TEST and SE Labs for protection, performance and false positives — so the claims we make about detection are third-party evidenced, not marketing.

FAQs

Common questions

Can this replace our current antivirus?

Yes. We remove the legacy product during onboarding and replace it with a single integrated agent that covers anti-malware, anti-ransomware, device control and vulnerability assessment.

Will it slow down our machines?

One agent replaces three or four, and scanning is offloaded and scheduled. In most estates we see a performance improvement after migration.

Does it protect servers as well as laptops?

Yes — Windows and Linux servers, virtual machines and workstations are all covered under the same policy framework.

What happens if ransomware still gets through?

We coordinate endpoint containment and remediation with the separate backup and recovery service, helping restore clean business data where required.

Book a Free Endpoint Security Review

Tell us about your users, devices, sites and requirements for a tailored recommendation.