Services /Managed Detection and Response (MDR)

Managed Detection and Response (MDR)

Automated security monitoring watches your estate 24/7, with expert review and response during agreed service hours.

Overview

What we deliver

NG TELECOM provides 24/7 automated monitoring and alerting, with expert triage, threat hunting, containment and recovery delivered during agreed service hours and under an agreed response SLA.

  • 24/7 automated monitoring and alerting
  • Proactive threat hunting
  • Incident containment and remediation
  • Guided recovery from clean backups
  • Monthly reporting and posture reviews
  • Documented escalation and response SLAs
Security monitoring and threat detection dashboard
Problems we solve
  • No automated monitoring outside working hours
  • Nobody in-house to triage security tooling
  • Insurers and clients asking for 24/7 monitoring
  • Incidents discovered days after the fact

Outcomes

What you can expect

Threats detected promptly for documented escalation

Security expertise without hiring

Evidence for insurance and audits

At a glance

Managed Detection and Response (MDR) explained

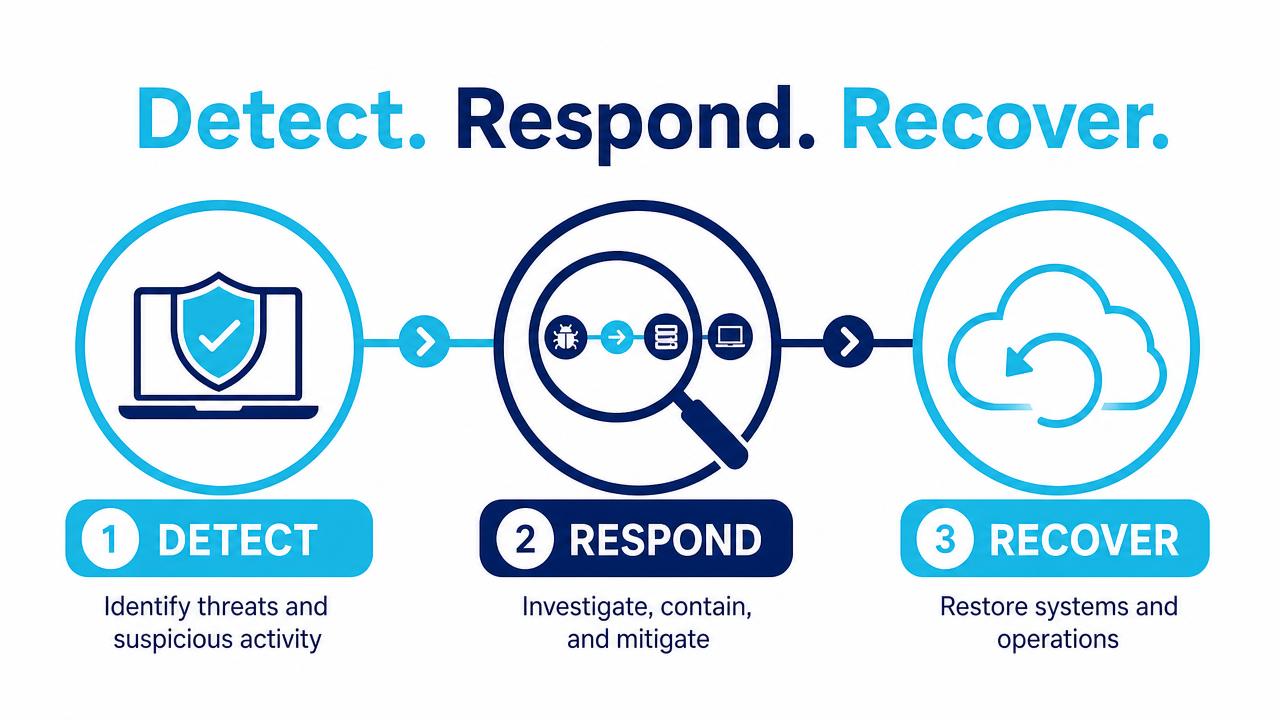
Detect, respond and recover stages of NG TELECOM managed security

How NG TELECOM detects, responds to and recovers from an attack.

In depth

How the service works

24/7 automated security monitoring without an in-house SOC

Continuous automated monitoring and alerting improve visibility outside working hours. Expert triage, proactive threat hunting and hands-on containment are delivered during agreed service hours under a documented response SLA.

Investigation, response and recovery — not just a phone call

A weak MDR emails you an alert. Ours contains the threat: isolate the workload, kill the process, remove persistence, block the indicator across the estate, then recover the affected data from backup and confirm the environment is clean before it goes back into service.

Threat research behind the service

Detection content is maintained by a dedicated threat research unit tracking active ransomware groups, malware families and exploited vulnerabilities, so new techniques become new detections without you filing a request.

Reporting your board and insurer will accept

Monthly reporting covers incidents raised, mean time to detect and respond, threats contained, coverage gaps and the posture improvements we recommend next. It is written to be readable by a director and detailed enough for an audit.

FAQs

Common questions

What is your response time?

Response SLAs and support hours are agreed in the service schedule by severity. Automated monitoring and alerting continue 24/7, but human technical support is not staffed around the clock.

Do you replace our IT team?

No. MDR sits alongside internal IT or our managed IT service and handles security detection and response specifically.

What does the onboarding look like?

Agent deployment and tuning typically takes one to two weeks, followed by a baselining period before full SLAs apply.

Will you also help after an incident?

Yes — containment, recovery from clean backups, root-cause write-up and the remediation plan are all part of the service.

Talk to Our MDR Team

Tell us about your users, devices, sites and requirements for a tailored recommendation.